TL;DR
Error 525: SSL Handshake Failed is a server-side error specific to Cloudflare. It means Cloudflare was able to contact your origin web server, but the two could not establish a secure TLS/SSL connection.
Key Takeaways:
- It’s a server-side error. The problem sits between Cloudflare and your origin server, not in the visitor’s browser or device.
- Only Cloudflare-proxied sites show it. Error 525 is a Cloudflare-specific status code, not a standard HTTP error.
- Common causes: a missing or misconfigured SSL certificate on the origin, port 443 closed or blocking Cloudflare IPs, no SNI support, or mismatched cipher suites and TLS versions.
- It’s often triggered by the SSL mode. Setting Cloudflare to Full or Full (strict) while the origin can’t serve HTTPS properly commonly causes it.
- Site owners fix it, not visitors. The fix is on the origin server or in Cloudflare’s SSL/TLS settings.
- Don’t confuse it with 526. Error 526 means the origin’s certificate is invalid; 525 means the handshake never completed at all.
SSL-enabled websites are essential for cybersecurity; SSL Handshake plays a key role. The SSL Handshake establishes a secure connection between a web client and a web server to protect sensitive information from malicious actors intercepting or tampering with it.
However, users might encounter an SSL handshake failed error message during this process.
To understand the SSL handshake failure error message, it is important to examine the SSL handshake process thoroughly.
What is an SSL/TLS Handshake?
SSL Handshake is a process that involves three essential functions: algorithm agreement, certificate exchange, and the exchange of cryptographic keys with the help of a shared algorithm.
The server and client agree on one of the two shared algorithms and exchange cryptographic keys using an SSL certificate to encrypt client-server communication.
It also authenticates the server by checking the SSL certificates. Thus, it helps ensure the client is a server, not an imposter. However, often, a glitch happens during this handshake, resulting in an ‘SSL handshake failed’ error message.
Let us discuss the error message in detail.
What is the SSL Handshake Failed Error Message?
TLS Handshake Failed Error comes up when a client or server cannot establish a secure connection. It is called the SSL Handshake 525 Failed. It can happen for multiple reasons- sometimes due to some issue at the client’s end and sometimes from the server’s end.
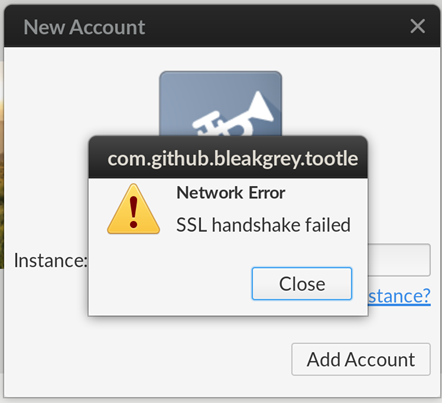
This error message might come up for different reasons based on the client application users use or the server they are trying to connect with. For example, an error in GitHub looks like this:
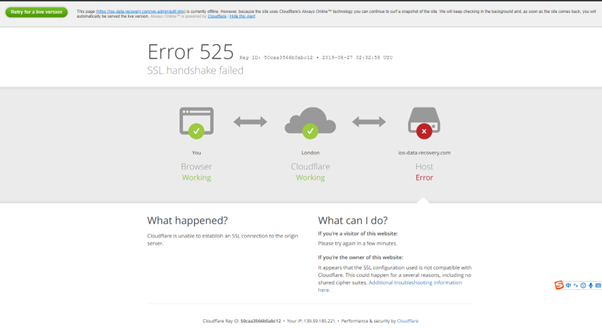
However, an error 525 on Cloudflare will look something like this:
So what are the reasons that result in the error? Let’s find out.
What Causes SSL Handshake Failure?
There are multiple reasons; here are some of the most common ones:
The Local Device has the Wrong Date or Time
One of the steps in the SSL/TLS Handshake process is for the browser to verify the validity of the SSL certificate. To check the certificate’s validity period, a web browser or server needs to define the “valid from” and “valid until” fields in the certificate.
If the date and time on the device are incorrect, the browser may incorrectly determine that the certificate is invalid, causing the SSL/TLS Handshake to fail.
It is because the client cannot verify the validity of the certificate. The validity period of the certificate enables its use.
The certificate has a validity period during which it can be used. If the purchased SSL certificate is expired or invalid, the client will reject it. Thus, the SSL Handshake will fail.
The issuing certificate authority (CA) creates and signs a timestamp in an SSL certificate. If the date and time on the client device are incorrect, it will not match the timestamp, causing the SSL Handshake to fail.
The Browser Doesn’t Support the Latest SSL Protocol
It occurs when the browser and server cannot negotiate a standard SSL protocol. This issue can occur if the browser does not support the latest SSL protocol and the server only allows connections using the latest protocol.
In this scenario, the browser cannot establish a connection and displays the error message.
The error message can also pop up if the SSL certificate is invalid or not trusted by the main server, or if there is a problem with the SSL/TLS configuration on the server.
Your SSL Certificate is Invalid
The central server verifies the SSL certificate before establishing a secure, encrypted connection. It will not establish a secure connection with the server if it does not recognize the certificate as valid.
For example, A self-signed certificate will not be trusted because a trusted certificate authority does not sign it. A secure connection cannot be established if the certificate has expired.
Issue with the Server Name Indication (SNI) Configuration
SNI is an SSL protocol extension that allows a web server to host multiple SSL-enabled websites with different domain names on the same IP address. When the Browser sends the requested domain name during the Handshake process, the server uses this information to select the correct SSL certificate to present to the Browser.
Improper server configuration to use SNI may prevent it from matching the requested domain name to the correct SSL/TLS certificate, resulting in a failed SSL handshake.
If the web browser does not support SNI, the SSL Handshake may fail even if the server is configured to use it.
Issue with Content Delivery Network (CDN)
A CDN is a distributed server system that delivers web content to a user based on their geographic location.
So when a user tries to access a website via a CDN, the handshake process occurs between the edge server of the CDN and the user’s Browser. If there is an issue with the CDN’s SSL configuration, the SSL Handshake will fail, and the user will see an SSL Handshake error message.
The issue could arise from an incorrect certificate, an incorrect SSL certificate chain, or a certificate that the browser does not trust.
If we don’t configure the CDN correctly to forward the Handshake to the origin server, it will show an error message.
These are some common reasons why error 525 comes up. Let us discuss how to fix it.
How to Fix the TLS/SSL Handshake Failed Error 525 as an Administrator?
If you are the site owner or have admin access, you can fix the SSL Handshake 525 Error in different ways. Here are some of them.
Check Your Cloudflare SSL/TLS Mode
Error 525 frequently comes right down to a battle between Cloudflare’s encryption mode and what your foundation server can actually manage.
- In your Cloudflare dashboard, open SSL/TLS → Overview and verify which encryption mode is active.
- Full and Full (strict) need HTTPS on the origin: Both modes require your server to just accept secure connections on port 443.
- Full (strict) additionally requires a legitimate, trusted, unexpired certificate.
- Use Flexible with care: Flexible stops the mistake by way of connecting to your server over simple HTTP.
If your server forces HTTPS, although, it is able to trigger limitless redirect loops, and the link to your beginning stays unencrypted. Treat it as a stopgap, now not a restore.
Confirm Your Origin Certificate Works
- Make sure an energetic, unexpired SSL certificates is hooked up and certain in your area on the server.
- Test without Cloudflare: Pause Cloudflare or switch your DNS document to DNS best (grey cloud), then go to https://yourdomain.Com. A browser SSL caution means the hassle is for your host, no longer Cloudflare.
- Get a loose certificate: If you don’t have one, generate a unfastened Cloudflare Origin CA certificates from the dashboard and installation it on Apache, Nginx, or cPanel.
Update Your System Date and Time
Correcting the date and time on a device could fix this if the error is related to the certificate validation process, specifically if the browser is incorrectly determining that the certificate is not valid due to the incorrect date and time.
While this solution may not guarantee a fix, investigators should also examine other causes of the error.
Check if the SSL Certificate Is Valid, Configure the Browser for the Latest SSL Protocol Support
Checking if your SSL certificate is valid and configuring your browser for the latest SSL protocol support can fix this error and establish a secure connection with the server. However, the error must be related to the certificate validation process or the SSL protocol version.
Ensure that your Server is properly configured to support SNI
You need to ensure your server is appropriately configured to support SNI. The SNI configuration involves some major issues, such as incorrect SNI configuration, missing SNI configuration, or missing domain names in the SNI configuration.
You also have to check that both your client-server and central server support SNI, as sometimes the latter do not support it.
Fixing Protocol Mismatch
The web server administrators can fix the protocol mismatch by configuring the web server and the client server to use the same SSL protocol. This allows them to establish a secure connection.
Web server admin can configure the browser to support the latest SSL protocol or configure the server to support older SSL protocols that it supports.
Also Read: How to Resolve ERR_SSL_PROTOCOL_ERROR in Chrome?
Check that your CDN or load balancer forwards the SSL protocol version your browser and server agree on.
How to Resolve Error 525 as a Website Visitor?
Error 525 is a server-side problem, so visitors can’t fix it directly. The failed connection is between Cloudflare and the website’s server, not your device. A few quick checks can still help you confirm that and work around it.
- Refresh the page: The error is sometimes temporary. Wait a minute and reload (Ctrl + F5 or Cmd + Shift + R).
- Try another browser or device: If the error appears everywhere, the site itself is the problem, not your setup.
- Clear your browser cache: This rules out a stale cached copy of the error page.
- Check Cloudflare’s status: Visit cloudflarestatus.com to see if a wider outage is affecting sites.
- Contact the website owner: Let them know you’re seeing “Error 525: SSL handshake failed,” along with the time it happened. Only the owner or their host can fix it.
These are some ways to fix the TLS handshake failed Cloudflare error message.
Conclusion
As SSL Handshake plays a crucial role in keeping data in transit secure, users must understand what the SSL Handshake fail 525 error means and how to fix it. By following the fixes we have mentioned, you should be able to resolve the issue and establish a secure connection.
Frequently Asked Questions
What does TLS Handhske failed mean?
SSL/TLS handshake failed error means that the secure connection between a client (browser, app, API client, etc.) and a server could not be completed.
What does error code 525 imply?
It means Cloudflare couldn’t complete a stable SSL/TLS handshake with the website’s origin server. The visitor reached Cloudflare efficiently, but Cloudflare couldn’t establish an encrypted connection to the server in the back of it.
Is errors 525 caused by Cloudflare or my server?
In almost every case, the issue is at the beginning server. Common culprits are missing or misconfigured SSL certificates, port 443 being closed, or unsupported TLS settings. Cloudflare is just reporting the failure.
Can an internet site visitor restore 525 code?
No. Visitors can refresh the page or strive later, but handiest the web site proprietor or hosting issuer can restore the server or Cloudflare configuration.
What is the difference between 525 and 526 error code?
Error 525 means the SSL handshake failed. Error 526 means the handshake labored; however, Cloudflare rejected the foundation’s certificate as invalid, expired, or untrusted under Full (strict) mode.
Will switching Cloudflare to Flexible SSL resolve error 525?
It commonly makes the error disappear, due to the fact that Cloudflare then connects to your server over HTTP. However, site visitors between Cloudflare and your server will become unencrypted, and it is able to cause redirect loops if your server forces HTTPS. Use it only as a transient workaround.
Can a firewall cause 525?
Yes. If your server firewall or security plugin blocks Cloudflare’s IP ranges on port 443, the handshake can’t complete. Allowlisting Cloudflare’s posted IP addresses resolves this.
How do I take a look at whether or not my beginning server’s SSL is working?
Temporarily set your DNS record to “DNS most effective” in Cloudflare and cargo your web site over HTTPS. You can also run openssl s_client -connect YOUR_SERVER_IP:443 -servername yourdomain.Com to check the handshake at once.

Fix Not Secure Browser Warnings
Immediately Fix Insecure Site and Mixed-content Warnings in Browsers by Adding Trusted SSL Certificate to your Website!
Buy SSL/TLS Certificate Now